London, U.K., September 22, 2026
- Gartner client? Log in for personalized search results.
Gartner Security & Risk Management Summit 2026 London: Day 1 Highlights
It’s not too late to join the conference
Overview
We are bringing you news and highlights from the Gartner Security & Risk Management Summit, taking place this week in London. Below is a collection of key announcements and insights coming out of the conference.
On Day 1 of the conference, we are highlighting the opening keynote, exploring why public sector AI investments often fail to deliver ROI and highlighting the outlook for cybersecurity threats. Be sure to check this page throughout the day for updates.
Key Announcements
Gartner Opening Keynote: Seize the Moment
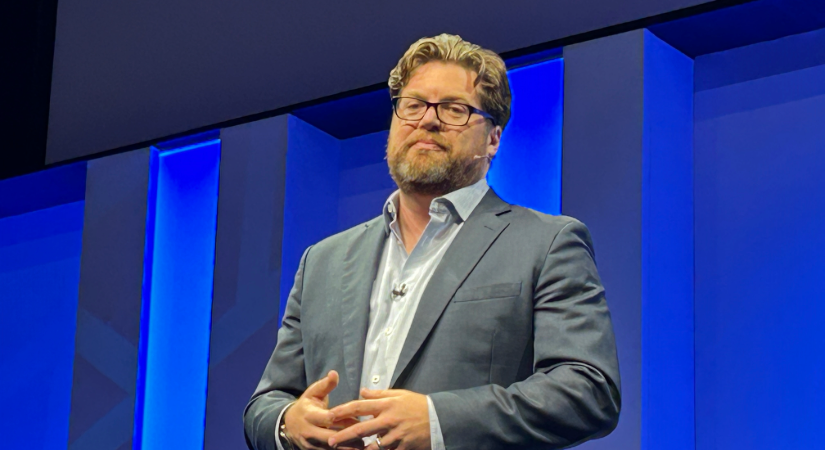
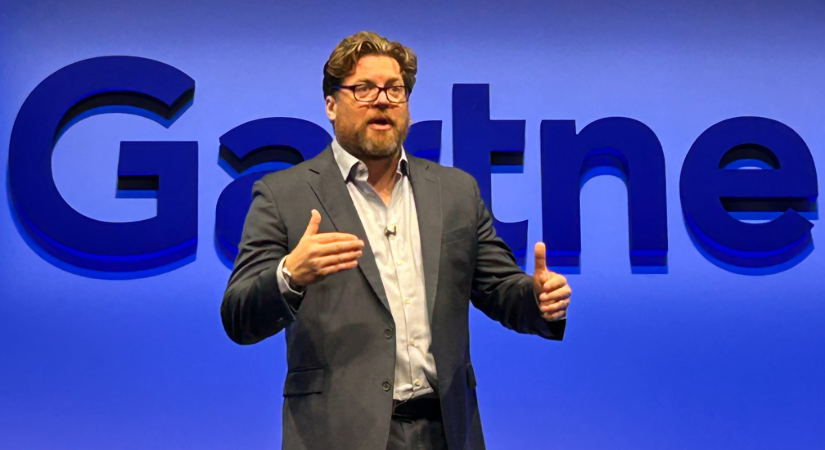
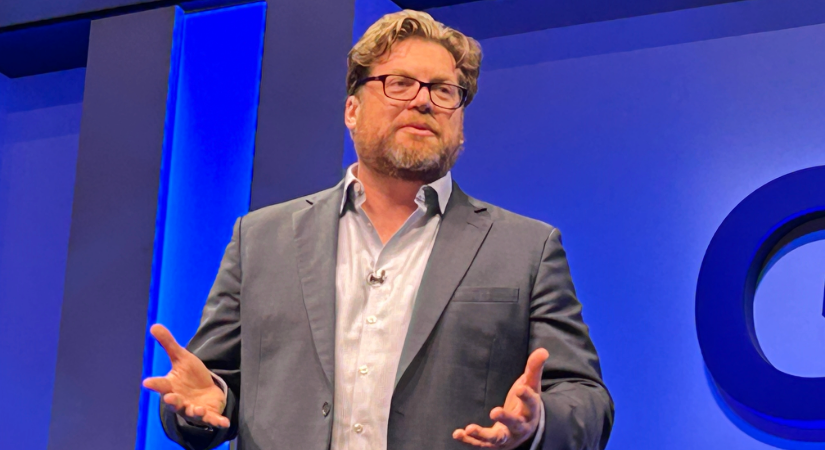
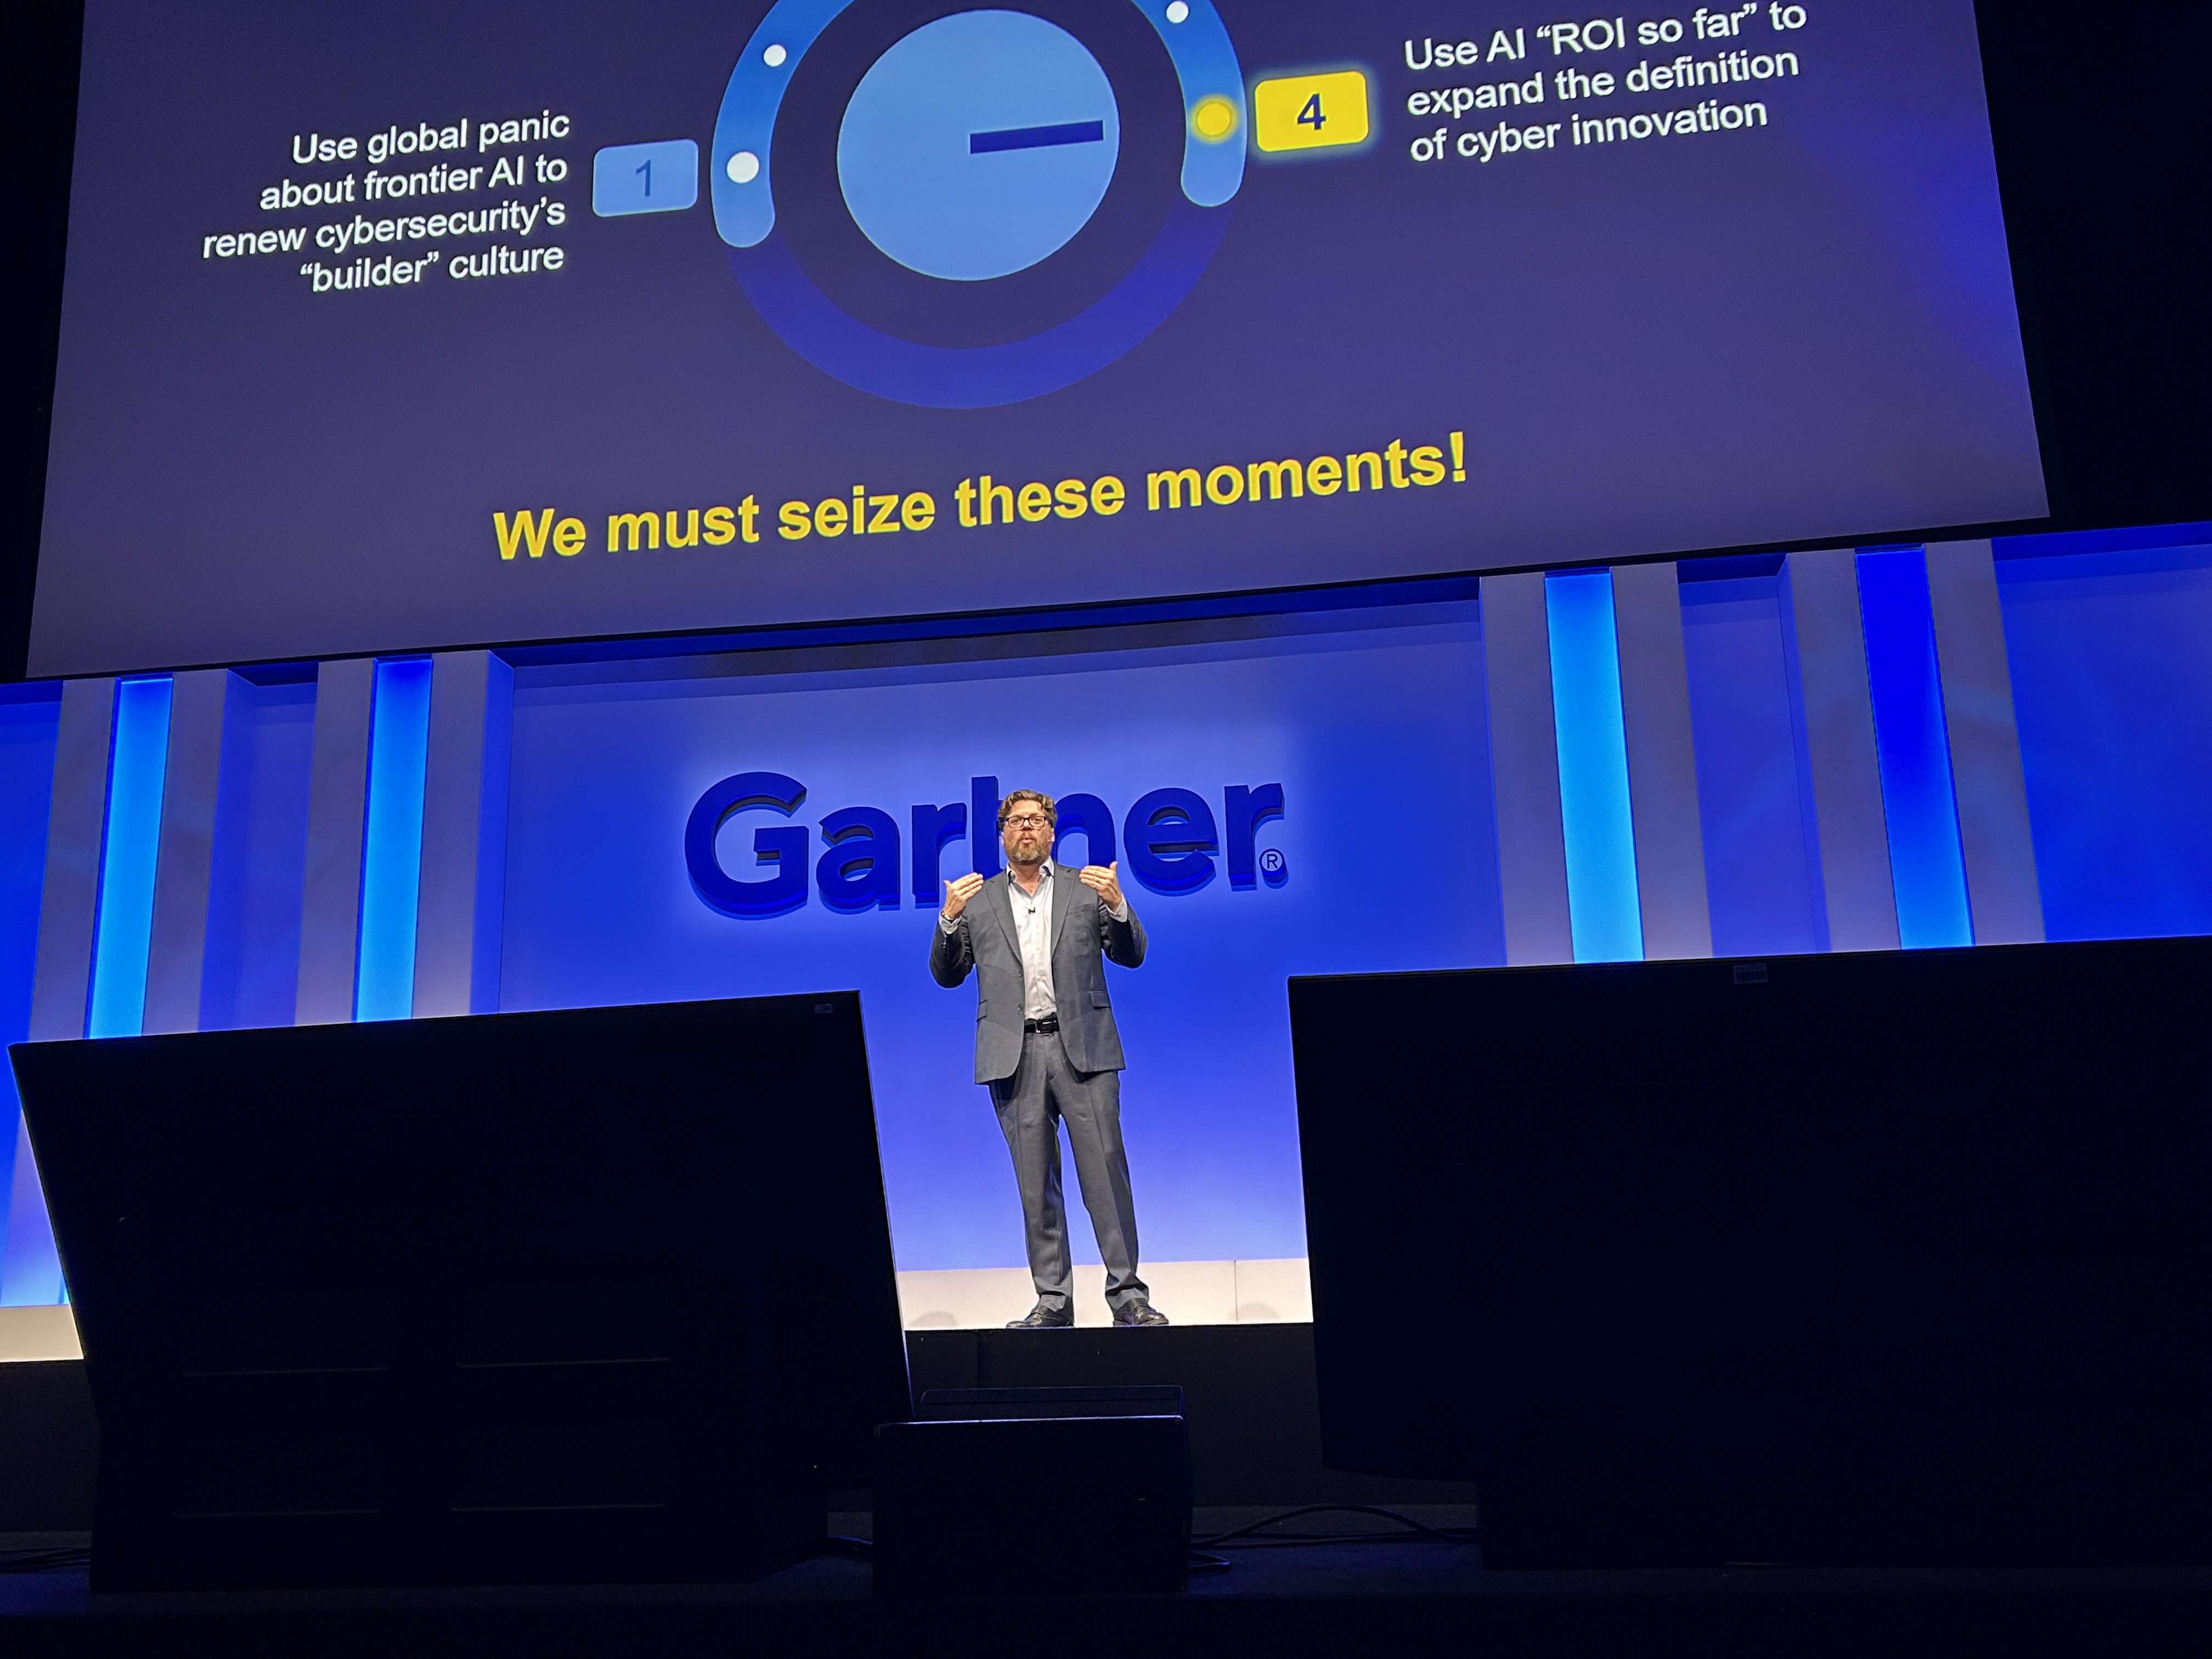
Presented by Christopher Mixter, Distinguished VP Analyst, Gartner
CISOs must rethink how they lead security, identity, and innovation as AI accelerates both opportunity and disruption. In the opening keynote, Christopher Mixter, VP Analyst at Gartner, explored four opportunities for chief information security officers to improve the effectiveness of their cybersecurity programs.
Key Takeaways
Is Dark AI The Apocalypse or Just Brilliant Marketing? “Frontier AI models do present dangers, but they also create advantages for cybersecurity teams over the attackers. Ignore the vendor/media doom-hype and show your executives that you are the right leader for this moment.”
Enterprise Investment in AI to Modernize IAM: “As customer, constituent, and supplier interactions become increasingly agent or even just machine based, position IAM modernization as an opportunity to show how IAM can be an accelerant in your company.”
Normalization of Cyberattacks to Redefine How We Win: “Cyberattacks have become a normalized feature of modern business. Resilience, not prevention, is the strategy organizations can use to win.”
Set Your Cybersecurity Team Up as World Class Innovators: “Measure cybersecurity innovation. Share and recognize it to help adapt, optimize, become more agile, or increase the scalability of your team. Use the enterprise rush to AI to recommit cybersecurity’s culture of solution-building.”
Journalists can receive additional information and/or request an interview with Christopher Mixter by contacting Laurence Goasduff at laurence.goasduff@gartner.com.
What Public Sector Leaders Are Getting Wrong About AI (And What They Must Do Now)
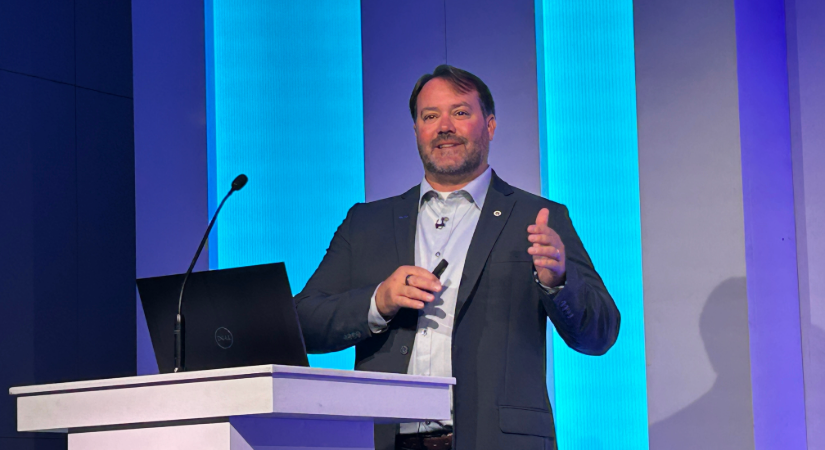
Presented by Michael McFerron, Sr Director Analyst, Gartner
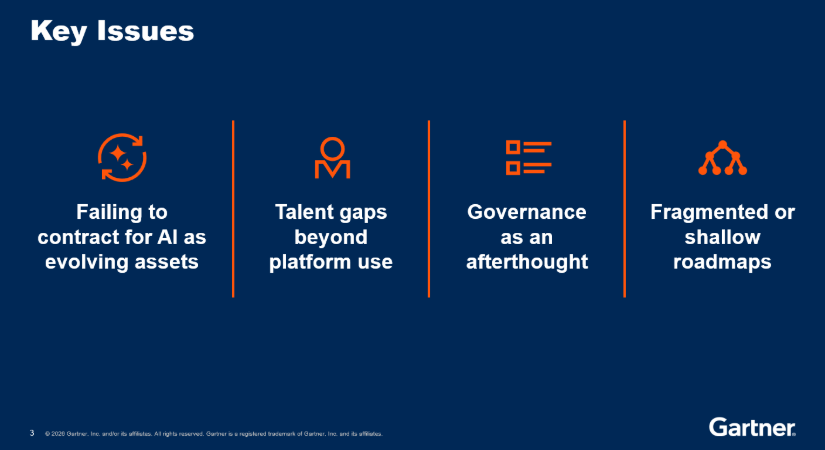
Public sector AI investments often fail to deliver return on investment (ROI) due to a narrow focus on buying tools and ill-defined goals. In this session, Michael McFerron, Sr Director Analyst at Gartner, explored why public sector AI initiatives often fall short and outlined how technology leaders must adopt an ecosystem-focused AI strategy that aligns data and analytics, talent, governance, and contracts to drive real mission impact.
Key Takeaways
- The four critical barriers limiting AI ROI in the public sector are static contracting, talent gaps, inadequate governance, and siloed roadmaps.
“Government leaders should move beyond static AI procurement by establishing contracts that govern the entire AI model lifecycle, including retraining requirements and transparency standards.”
“Although government organizations have AI users, they lack informed buyers and security stewards. Building internal AI literacy and shifting the workforce from AI users to AI evaluators can help ensure vendor accountability and strengthen defenses against adversarial threats.”
“Prioritizing short-term AI wins without mission alignment can lead to wasted resources, redundant systems, and overreliance on off-the-shelf commercial tools. Break down departmental silos and align AI initiatives with mission outcomes and overall organizational objectives to deliver maximum impact.”
Journalists can receive additional information and/or request an interview with Michael McFerron by contacting Laurence Goasduff at laurence.goasduff@gartner.com.
Outlook for Cybersecurity Threat Landscape: Prioritizing Threats With Gartner's ThreatScape
Presented by Eric Grenier, Sr Director Analyst, Gartner
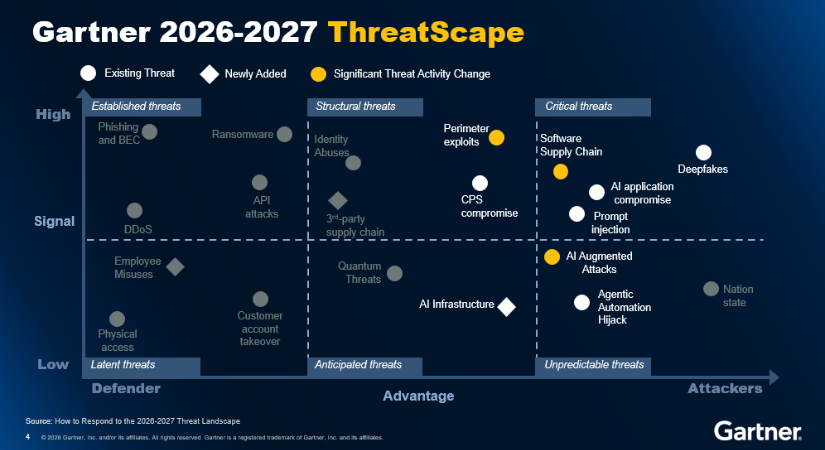
The cybersecurity threat landscape is a moving target making it increasingly difficult for organizations to address every risk with limited resources. In this session, Eric Grenier, Sr Director Analyst at Gartner, discussed the 2026-2027 threat landscape (ThreatScape) to help organizations optimize their prediction and prevention, enhance detections, and prepare for new and emerging threats.
Key Takeaways
“There are four critical and unpredictable threats where attackers hold a significant advantage to successfully exploit weaknesses in targeted organizations.”
AI Application Compromise: “AI application compromise is an anticipated threat as attackers target the growing number of production-ready public-facing and internal enterprise AI tools.”
Identity Impersonation Using Deepfakes: “The advent of GenAI has dramatically increased the volume, fidelity and accessibility of deepfake creation across voice, video, and images, as pre-recorded artifacts or generated in real-time.”
Software Supply Chain Threats: “Software supply chain risks are escalating as attackers increasingly compromise third-party components, open-source libraries and development tools used to create enterprise applications.”
Prompt Injection: “Prompt injection is a cybersecurity threat targeting AI systems, especially those using large language models (LLMs). Attackers manipulate prompts to alter the AI’s behavior, causing it to leak sensitive information, perform unauthorized actions, or bypass controls.”
Journalists can receive additional information and/or request an interview with Eric Grenier by contacting Laurence Goasduff at laurence.goasduff@gartner.com.
It’s not too late to join the conference


About Gartner
Gartner (NYSE: IT) delivers actionable, objective business and technology insights that drive smarter decisions and stronger performance on an organization’s mission-critical priorities. To learn more, visit gartner.com.